[Analysis]
Jaguar Land Rover cyber attack: a five-week production shutdown
One attack stopped production for five weeks and, by one estimate, cost the UK economy £1.9 billion, much of it lost by suppliers who were never attacked. The lesson is about recovery as much as prevention.
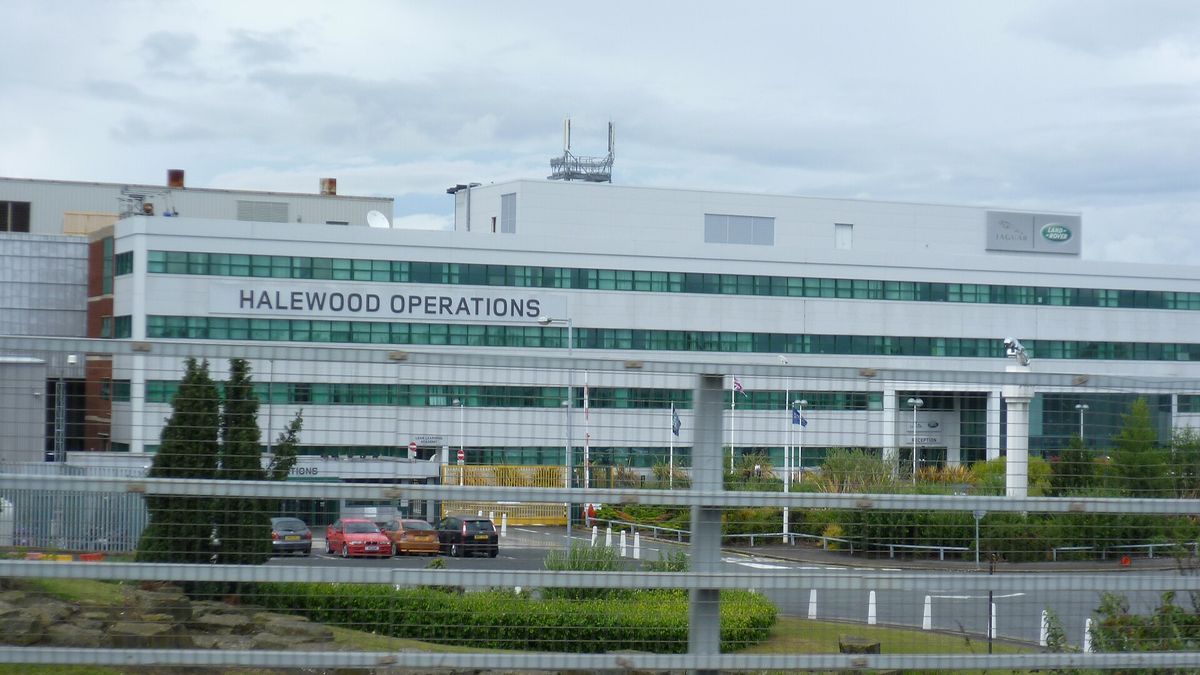
At the end of August 2025 Jaguar Land Rover (JLR) was hit by a cyber attack that forced it to shut down its IT systems. Production stopped on 1 September at its three main UK plants, in Solihull, Wolverhampton and Halewood, and tens of thousands of staff were told to stay at home. A phased restart began on 6 October at the Wolverhampton engine plant, more than five weeks later.
The damage did not stop at JLR’s gates. Car manufacturing runs on just-in-time supply, and the company’s suppliers, many of them small and medium-sized businesses, were left with nobody to deliver to. The government stepped in with a guarantee on a £1.5 billion commercial loan to JLR, intended in part to keep money flowing down the supply chain.
Counting the cost
The Cyber Monitoring Centre, an independent body that rates the impact of UK cyber events, classified the incident as a Category 3 systemic event. It estimated the cost to the UK economy at around £1.9 billion (within a modelled range of £1.6 to £2.1 billion), with more than 5,000 organisations affected. The CMC’s view is that it appears to be the most economically damaging cyber event to hit the UK. Most of the cost was lost manufacturing output, at JLR and at its suppliers.
[One attack, thousands of businesses]
- JLR attacked; IT systems shut down
- Production stops at Solihull, Wolverhampton and Halewood
- Suppliers, many of them small businesses, left with nobody to deliver to
Five weeks without production, from 1 September to 6 October 2025.
The cost, as estimated by the Cyber Monitoring Centre
- £1.9 billion to the UK economy
- More than 5,000 organisations affected
Most of it was lost manufacturing output, at JLR and at suppliers who were never attacked themselves.
The NCSC’s public statement was brief: it was working with JLR to provide support, and it urged all organisations to make use of its free guidance, services and tools. The details of how the attackers got in have not been published by JLR or the NCSC, so we won’t guess.
Why this matters to small organisations
There are two lessons here, and the second is the less comfortable one.
First: your supplier’s incident is your incident. Thousands of businesses that were never attacked still lost weeks of revenue. It’s worth asking which of your customers and suppliers you could not trade without, and what you would do if one of them went dark for a month.
Second: recovery is where the money is lost. Most organisations will, at some point, have a serious incident. What separated a bad week from a catastrophic quarter here was how long it took to get systems back safely. That is decided long before an attack, by whether you have tested backups, a written plan, and a clear idea of which systems have to come back first.
What the NCSC and government recommend
In October 2025, government ministers, the NCSC and the National Crime Agency wrote to the chief executives and chairs of every FTSE 350 company. The letter asked for three things, and none of them is only for large firms:
- Have a plan to respond and recover. The government’s Cyber Governance Code of Practice is written for boards and directors, and asks them to own that plan. The NCSC’s Exercise in a Box is a free way to rehearse it.
- Sign up to the NCSC’s Early Warning service. It’s free, and it tells you about potential attacks and compromises affecting your own IP addresses and domains.
- Require Cyber Essentials in your supply chain. It’s the government-backed minimum standard, and asking suppliers to hold it (and holding it yourself) is one of the simplest ways to raise the floor.
To that we’d add the NCSC’s long-standing ransomware advice: keep recent, offline backups of the data you can’t do without, and test restoring from them. A backup you have never restored from is a hope, not a plan.
Sources
- NCSC, Statement: incident impacting Jaguar Land Rover (September 2025)
- Computer Weekly, Jaguar Land Rover attack to cost UK £1.9bn, say cyber monitors (October 2025)
- British Retail Consortium, Ministers and NCSC letter to boards and directors (October 2025)
- NCSC, Mitigating malware and ransomware attacks
- NCSC, Cyber Essentials